Protect your business from phishing attacks with FIDO2

FIDO2 smart cards, security keys and readers from Universal Smart Cards. Specified for your environment, supplied from the UK and ready to enrol.

Hardware from HID GlobalYubicoHirsch (formerly Identiv)TaglioCHERRY
Why MFA

A password alone no longer protects your business

Many attacks don't break in. They log in. A stolen, guessed or reused password gives an attacker the same access as your employee. Multi-factor authentication (MFA) asks for a second proof of identity, so a password on its own is no longer enough.

43%

of UK businesses reported a cyber breach or attack in the last 12 months.

69%

of large businesses reported one, and 65% of medium-sized businesses.

53%

of UK businesses don't report having any two-factor authentication in place for their networks or applications.

Source: DSIT, Cyber Security Breaches Survey 2025/2026 (April 2026). The 53% is the share of businesses not reporting any two-factor authentication requirement for networks or applications (47% do).

01

Stolen passwords stop working

A leaked or reused password can't open an account without the second factor, so credential stuffing and password spraying fail.

02

Remote and cloud access is protected

Microsoft 365, VPN, remote desktop and SaaS apps get the same strong check, wherever your people sign in from.

03

Certification and insurance requirements met

Cyber Essentials requires MFA on cloud services, and since April 2026 not having it is an automatic fail. Cyber insurers commonly ask about it on applications and renewals.

04

Fewer resets, faster sign-in

With FIDO2 hardware, users tap a card or touch a key instead of typing passwords and codes, which can reduce lock-outs and password-reset requests.

Timeline

From headline breaches to hard deadlines

Since 2013, some of the most damaging breaches have started with people, not technology: a convincing email, a phone call or an approved login prompt. Now UK guidance, Cyber Essentials and Microsoft's own platform all favour passkeys over passwords and SMS codes.

Phishing breachesGuidance and regulationKey deadline
  1. Nov–Dec 2013Breach

    Target

    Attackers reportedly got in using credentials stolen from a refrigeration and HVAC contractor through malware-laden emails. Data from around 40 million payment cards was taken.

  2. Nov 2014Breach

    Sony Pictures

    US prosecutors allege spear-phishing emails to staff gave attackers access. Unreleased films, staff records and executive emails were leaked, including Spider-Man discussions with Marvel.

  3. Jul 2020Breach

    Twitter

    Attackers phoned staff posing as the internal IT help desk, captured their credentials on a fake login page, then targeted 130 high-profile accounts.

  4. Sep 2022Breach

    Uber

    An attacker with a contractor's stolen password triggered repeated MFA approval requests until one was accepted. Phishing-resistant MFA can't be approved from a remote prompt.

  5. Sep 2023Breach

    MGM Resorts

    The attack reportedly began with a call to the IT help desk from someone impersonating an employee. MGM estimated a negative impact of around $100 million on quarterly adjusted property earnings.

  6. Apr 2025Breach

    Marks & Spencer

    Attackers gained access through sophisticated impersonation involving a third party. Online orders were paused for about seven weeks, and M&S initially estimated a £300 million hit to operating profit before mitigation.

  7. 23 Apr 2026

    NCSC guidance

    The NCSC describes traditional MFA as phishable and is moving to recommend passkeys.

  8. 27 Apr 2026

    Cyber Essentials

    Under v3.3 (the Danzell question set), not using MFA on a cloud service where it is available is now an automatic fail, even where MFA is a paid option.

  9. 1 Sep 2026

    Microsoft Entra ID

    Microsoft begins switching on passkeys, and prompting registration, for Entra ID users who currently use SMS or voice verification.

  10. 11 Sep 2026

    EU CRA reporting begins

    Under the EU Cyber Resilience Act, manufacturers of hardware and software sold in the EU must report actively exploited vulnerabilities and severe incidents affecting product security.

  11. 1 Feb 2027

    SMS and voice codes retired

    Microsoft stops providing SMS and voice verification for MFA in Entra ID for most users. Global Administrators and external users follow on 1 July 2027. Organisations that still need SMS or voice must use their own telephony provider.

  12. 11 Dec 2027

    EU CRA fully applies

    The Cyber Resilience Act's main obligations, including security-by-design and lifecycle requirements, apply to products with digital elements placed on the EU market.

← Earlier breachesDrag, swipe or use the arrowsUpcoming deadlines →
In Parliament

UK Cyber Security and Resilience Bill

The Bill updates the Network and Information Systems Regulations 2018 and is at Report stage in the House of Lords (October 2026).

Follow the Bill →
  • Wider scopeMedium and large managed service providers, larger data centres, large load controllers and designated critical suppliers come into scope for the first time.
  • Faster incident reportingAn initial notification within 24 hours and a full report within 72 hours.
  • Stronger enforcementRegulators gain powers to inspect and request information, with turnover-based penalties.
  • AI risksIn October 2026 the government said it will look at how serious AI incidents and near misses are identified and reported under the regime.
Phishing-resistant MFA

Not all MFA is equal

Text-message codes, app codes and push approvals can still be phished. An attacker builds a convincing fake login page and relays the code in real time. The NCSC now describes traditional MFA as phishable. FIDO2 hardware is phishing-resistant by design.

Password only SMS or voice code Authenticator appcode or push FIDO2 card or key
Stops attacks with stolen passwords✕✓✓✓
Resists SIM swaps and SMS interception✕✕✓✓
Resists fake login pages✕✕✕✓
Works without a smartphone–Partlyvoice can use a landline✕✓
How users sign inType passwordWait for a text or callOpen app, copy or approveTap or touch, enter PIN
Hirsch uTrust FIDO2 GOV security key Touch to sign in
How it works

Tap, confirm, signed in

  1. 01

    Present your credential

    Tap a FIDO2 smart card on a reader, or plug in and touch a security key.

  2. 02

    Confirm it's you

    Enter a short PIN. It's checked by the card or key itself and never sent to the website.

  3. 03

    Signed in, securely

    The chip signs a one-time challenge with a private key that never leaves it. Each credential is bound to the genuine website, so a look-alike page gets nothing it can use.

FIDO2 cards and keys hold device-bound passkeys. They work with Microsoft Entra ID, Okta, Google Workspace and other services that support FIDO2.

Products

Authentication hardware we trust

Tell us about your users, devices and identity provider, and we'll specify the right mix of cards, keys, readers and keyboards.

Brands
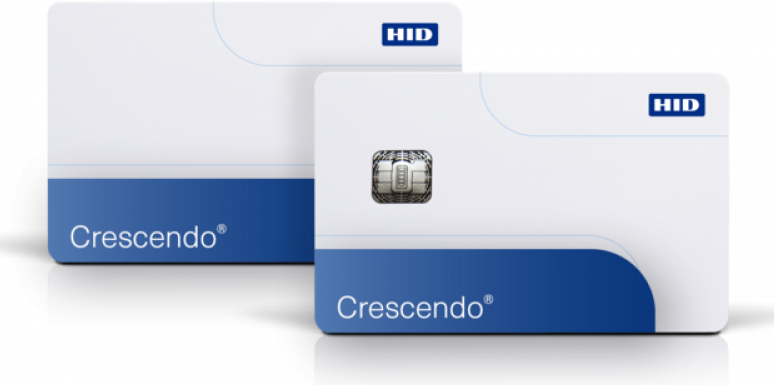
Converged access HID Crescendo converged access cards
HID Crescendo

One card. Every door, every desktop.

Security used to mean locking doors and windows. Now it means protecting every login too. A converged card carries your building-access technology and a FIDO2 passkey on the same credential, so the card that opens the door also signs your people in.

Sign-in
FIDO2 passkeys for Microsoft Entra ID and other FIDO2-enabled identity providers. PIV and PKI for Windows smart card logon.
Door access
HID Crescendo cards can be built with HID Prox (125 kHz), iCLASS, Seos, MIFARE Classic or MIFARE DESFire to work with the readers you already have.
At the desk
Users tap the card on an HID OMNIKEY 5022 for FIDO2 sign-in. For PKI logon on the contact chip, the CHERRY Smart Board 1150 puts the reader in the keyboard.
Personalisation
Printed with your artwork and photo ID, and encoded in our UK bureau.
Lifecycle
One credential to issue, update and revoke when people join, move or leave.
FIDO2Physical accessPhoto IDSingle credential
Request a converged card quote →
Smart cardHID Crescendo 4000 Contactless
HID Global

HID Crescendo 4000 Contactless

FIDO2 and PKI smart card, with an optional HID Seos, iCLASS or MIFARE build for door access. FIDO2, PIV and PKI in one credential. Works with Microsoft Entra ID and other FIDO2-enabled identity providers.

ContactlessFIDO2PIVFIPS 140-3 edition
Smart cardHID Crescendo 4000 Dual Interface
HID Global

HID Crescendo 4000 Dual Interface

Contact and contactless in one card. Built with a door-access technology, one credential covers IT sign-in and building access. Works with Microsoft Entra ID and HID ActivClient.

Dual interfaceFIDO2PIVFIPS 140-3 edition
Smart cardTaglio PIVKey C915
Taglio

Taglio PIVKey C915

Dual interface PKI smart card and successor to the C910. For Windows logon, Microsoft CBA, RDP, digital signing, email encryption and SSH. Read-only with the Windows in-box PIV driver; full read/write with the PIVKey minidriver.

Dual interfacePKIPIVCC EAL6+ chip
Smart cardTaglio PIVKey C980 v2 Enterprise
Taglio

Taglio PIVKey C980 v2 Enterprise

Dual interface PKI card on the NXP JCOP P71 chip. Supports all four PIV certificate slots, plus up to 16 more on Windows through the PIVKey minidriver. Works with Microsoft CA and Versasec vSEC:CMS.

Dual interfacePKINXP JCOP P71
Security keyHID Crescendo Key v3 USB-C
HID Global

HID Crescendo Key v3 USB-C

Security key with USB-C and NFC. Passkeys, PIV certificates and one-time passcodes in one key, with shared or separate PINs. FIDO2-certified Enterprise edition; a FIPS 140-3 edition is also available.

USB-CNFCFIDO2PIVFIPS 140-3 edition
Security keyHID Crescendo Key v3 USB-A
HID Global

HID Crescendo Key v3 USB-A

The same passkey, PIV and one-time passcode support with a USB-A connector and NFC, for older laptops and desktops. PINs can be reset centrally with HID Crescendo Manager or HID CMS. Ask us about availability.

USB-ANFCFIDO2PIV
Security keyYubiKey 5 NFC
Yubico

YubiKey 5 NFC

FIDO2, U2F, OTP, PIV and OpenPGP in one key. USB-A, with NFC for tap sign-in on iPhone and Android.

USB-ANFCFIDO2PIV
Security keyYubiKey 5C NFC
Yubico

YubiKey 5C NFC

The same protocols with USB-C and NFC. Suits modern laptops, and NFC-enabled iPhone and Android devices.

USB-CNFCFIDO2PIV
Security keyYubiKey 5 Nano
Yubico

YubiKey 5 Nano

Compact key designed to stay in a USB-A port. Suits fixed workstations and kiosks.

USB-ANanoFIDO2PIV
Security keyHirsch uTrust FIDO2 NFC+
Hirsch

Hirsch uTrust FIDO2 NFC+

FIDO2, U2F, PIV and OTP security key with USB-A and NFC, formerly sold under the Identiv brand. Configure with the free uTrust Key Manager.

USB-ANFCFIDO2PIV
Security keyHirsch uTrust FIDO2 GOV
Hirsch

Hirsch uTrust FIDO2 GOV

FIDO2 key for government and regulated sectors, in USB-A or USB-C, both with NFC. Built on a FIPS 140-3 validated chip, with validation of the key itself under way. Supports FIDO2, U2F, PIV and HOTP.

NFCFIDO2PIVFIPS 140-3 in process
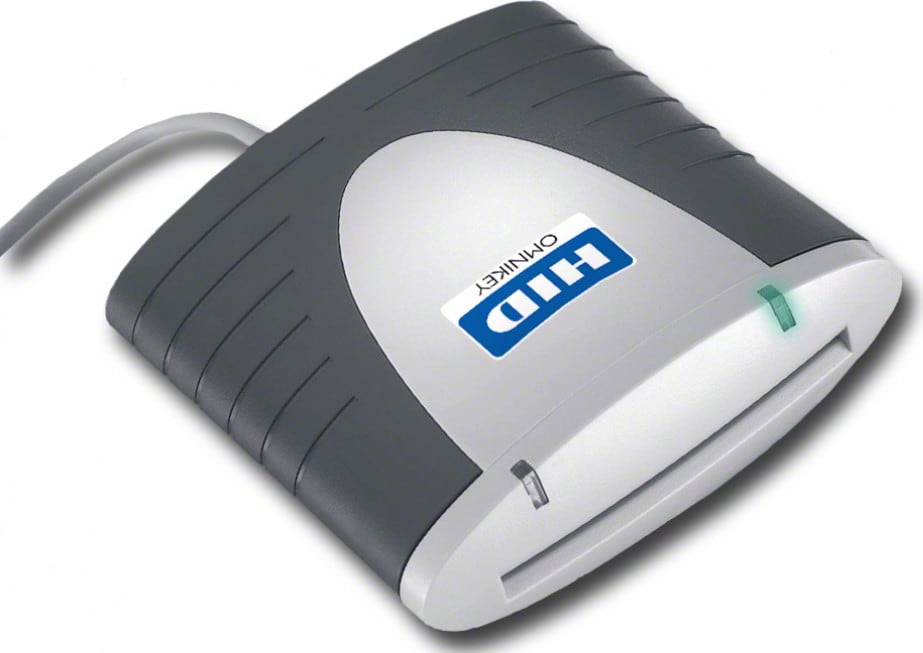
ReaderHID OMNIKEY 3121
HID Global

HID OMNIKEY 3121

USB contact smart card reader. Plug-and-play on Windows, macOS and Linux with no drivers. For contact PIV and PKI cards.

USB-AContactCCID
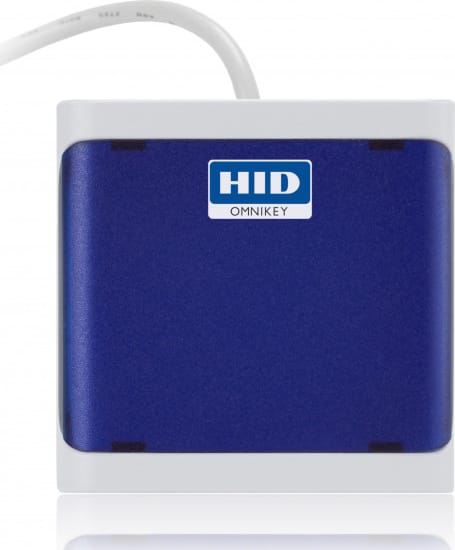
ReaderHID OMNIKEY 5022
HID Global

HID OMNIKEY 5022

USB contactless reader for tapping FIDO2 cards at the desk. No drivers needed. Reads iCLASS, MIFARE, DESFire and more.

USB-AContactlessFIDO2 compatibleCCID
ReaderHID OMNIKEY 5422
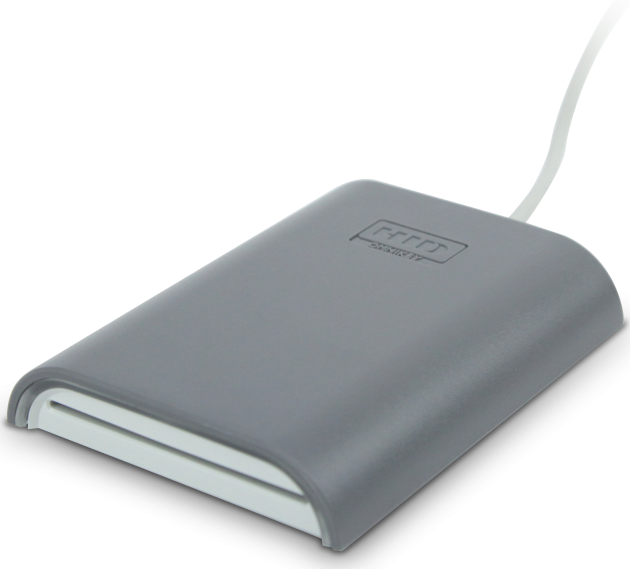
HID Global

HID OMNIKEY 5422

Contact and contactless in one reader, for estates that use both card types.

USB-ADual interfaceFIDO2 compatibleCCID
Fingerprint readerHID DigitalPersona 4500
HID Global

HID DigitalPersona 4500

Optical USB fingerprint reader for fingerprint sign-in with HID DigitalPersona software. Encrypts each fingerprint image and rejects fake fingers. Its compact metal casing suits hot desks and shared workstations.

USB-AFingerprint500 dpiEncrypted
ReaderHirsch uTrust 3700 F
Hirsch

Hirsch uTrust 3700 F

USB contactless reader for ISO 14443, MIFARE, DESFire and FeliCa cards, formerly sold under the Identiv brand. Plug-and-play on Windows, macOS, Linux and Android.

USB-AContactlessNFC
KeyboardCHERRY Smart Board 1150
CHERRY

CHERRY Smart Board 1150

Full-size wired keyboard with a contact smart card reader built in, so there is no separate reader on the desk. PC/SC and CCID compatible on Windows, macOS and Linux. For contact PIV and PKI cards.

USB-AContactCCIDUK layout
ReaderCHERRY Smart Terminal ST-1150
CHERRY

CHERRY Smart Terminal ST-1150

Compact USB contact smart card terminal with one-handed card insertion and very low power consumption. ISO/IEC 7816 and CCID for logon, network access and secure online transactions.

USB-AContactCCIDISO/IEC 7816
Standards

Built for regulated environments

Hardware that helps you meet the frameworks your auditors, insurers and customers ask about.

UK guidance

NCSC

Phishing-resistant authentication in line with the NCSC's move towards passkeys.

Certification

Cyber Essentials

Helps you meet the requirement for MFA on cloud services. Since April 2026, missing MFA where it is available is an automatic fail.

Information security

ISO/IEC 27001

Supports the standard's access control and secure authentication controls.

Validated hardware

FIPS 140

FIPS 140-3 validated editions of HID Crescendo cards and keys for organisations that require them.

Assurance level

NIST SP 800-63B AAL3

Phishing-resistant hardware authenticators with non-exportable keys, the type AAL3 calls for. Ask us which options suit your assurance requirements.

Risk

Cyber insurance

Cyber insurers commonly ask about MFA on applications and renewals. Phishing-resistant MFA strengthens your answer.

FAQ

Common questions

Can't see your question? Call +44 (0)333 700 0078 or email sales@usmartcards.com.

What is FIDO2?

FIDO2 is an open standard from the FIDO Alliance (CTAP2) and W3C (WebAuthn) for passwordless, phishing-resistant sign-in. It uses public-key cryptography: the private key stays on the card or key, and the service only ever stores a public key, so there is no shared secret to steal.

Is a FIDO2 key the same as a passkey?

A passkey is a FIDO2 credential. Cards and security keys store device-bound passkeys on a secure chip, so the credential can't be copied or synced to another device. That's why many organisations choose hardware for staff and administrator accounts.

Will it work with Microsoft Entra ID and Microsoft 365?

Yes. Entra ID supports FIDO2 security keys and passkeys for Microsoft 365 and other connected apps, and for Windows sign-in on Entra-joined and hybrid-joined devices. Okta, Google Workspace and many other services also support FIDO2.

Do we need card readers?

Security keys plug into USB or tap on NFC-enabled phones, so they don't need a reader. FIDO2 smart cards are tapped on a contactless (NFC) reader, which is built into some laptops or available as a small USB reader such as the HID OMNIKEY 5022. For contact PIV and PKI cards, the CHERRY Smart Board 1150 keyboard has a reader built in, or the CHERRY ST-1150 sits neatly on the desk. We'll recommend the right combination for each user group.

Can the same card open our doors?

Yes. HID Crescendo FIDO2 cards can be built with HID Prox, iCLASS, Seos, MIFARE Classic or MIFARE DESFire, giving your people one card for the building and the desktop. For PKI-only estates, Taglio PIVKey C70 cards combine certificates with Prox or DESFire. Tell us what your door readers use and we'll match it.

What happens if someone loses their card or key?

Remove the lost credential from the user's account and issue a replacement. With Microsoft Entra ID, a lost card or key can't be used to sign in without its PIN, and repeated wrong guesses lock it. We recommend registering a backup method for each user.

How quickly will we get a quote?

Usually within one business day. The more you tell us about your users, devices and identity provider, the more precise the proposal will be.

Ready to move beyond passwords?

Tell us about your users, devices and identity provider. We'll come back with a specified, costed proposal, usually within one business day.

Request a quote